Singapore Airlines confirms possible exposure of 46,000 booking records
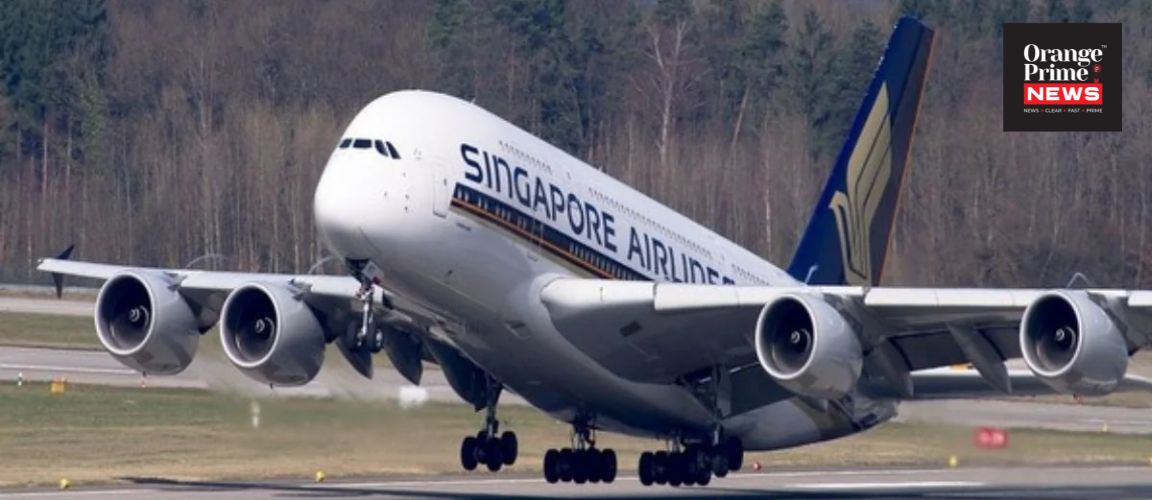
Singapore Airlines said on Tuesday that around 46,000 booking records may have been affected by a cybersecurity incident involving Amadeus, the technology provider that supports its reservation systems.
The airline's disclosure makes it the latest major international carrier to report potential exposure of customer information linked to the Amadeus breach.
According to Singapore Airlines, the information that may have been accessed includes passengers' names, booking reference numbers, travel itineraries and booking classes.
The airline also warned that additional personal information could have been exposed in a smaller number of records. For approximately 620 bookings, this potentially included email addresses, telephone numbers, travel document details and KrisFlyer membership numbers.
KrisFlyer is Singapore Airlines' frequent-flyer programme, making the possible exposure of membership information an additional concern for affected customers.
Payment information and bookings reportedly unaffected
Singapore Airlines said Amadeus had confirmed that bank account and credit card information had not been leaked in the incident.
The airline also stated that existing bookings had not been modified as a result of the breach.
This means the reported incident concerns the possible exposure of reservation and personal information rather than unauthorised changes to passengers' travel arrangements.
Singapore Airlines further clarified that its own information technology systems had not been breached. The incident involved its reservation technology provider, Amadeus.
The distinction is important because the airline's disclosure points to a security issue within a third-party technology environment rather than a direct compromise of its internal IT infrastructure.
Airline contacts affected passengers
Singapore Airlines said it was contacting customers whose upcoming travel plans could be affected by the incident.
As a precaution, the airline is arranging changes to booking reference numbers for affected passengers with future journeys.
Changing a booking reference can help reduce the risk of unauthorised access to reservation details, particularly when information such as a passenger's name and booking reference may have been exposed.
Customers whose records are involved are being contacted directly by the airline, according to its statement.
The company has not indicated that passengers need to cancel or change their travel plans because of the incident. It has also said that bookings were not altered.
Other international airlines report similar exposure
Singapore Airlines is not the only carrier to have reported possible customer data exposure connected to the Amadeus incident.
Cathay Pacific Airways, Japan Airlines and South Korea's Asiana Airlines have also disclosed that customer information may have been compromised.
Malaysia Airlines has separately said that some of its customer information could have been affected.
The disclosures indicate that the incident has potentially affected multiple airlines using Amadeus technology for reservation-related services.
In recent days, Cathay Pacific reported that information associated with approximately 53,000 bookings may have been affected. Japan Airlines disclosed potential exposure involving around 92,000 customers.
The figures refer to different airlines and reporting categories, so they should not be treated as directly comparable measures of the total number of affected individuals.
Amadeus acknowledges vulnerability in booking display environment
Amadeus said it had become aware of a vulnerability affecting a travel booking display environment.
However, the company did not respond to a question about the total number of customers whose information may have been affected.
The available information does not establish the full scale of the incident or explain precisely how the vulnerability was exploited.
As airlines continue assessing the potential impact, the incident has drawn attention to the cybersecurity risks associated with third-party technology providers that handle large volumes of passenger information.
Reservation platforms process sensitive details required for booking and managing journeys. A security weakness in such an environment can therefore have implications for multiple airlines and their customers.
What affected passengers should know
The information potentially exposed in the Singapore Airlines incident includes booking references and travel details, with a smaller number of records also potentially containing contact information, travel document details and frequent-flyer membership numbers.
Passengers who receive a notification from the airline should follow its instructions regarding revised booking references and other precautionary measures.
They should also be cautious about unexpected emails, text messages or phone calls claiming to offer refunds, booking assistance or travel updates. Personal information exposed in a data breach can potentially be used in targeted phishing attempts.
Passengers should verify any request for sensitive information through Singapore Airlines' official customer service channels rather than relying on links or contact details provided in unsolicited messages.
Third-party cybersecurity risks come under scrutiny
The Amadeus incident highlights the wider security challenges facing the global aviation industry as airlines increasingly depend on external technology providers.
Reservation systems connect airlines, travel agents and other service providers, making them central to the management of passenger journeys.
A vulnerability in one part of this interconnected system can potentially affect information held across multiple organisations.
For Singapore Airlines, the immediate priority is to notify affected customers, secure reservation records and minimise the risk of unauthorised access.
The airline has said its own IT systems were not compromised, payment information was not leaked and bookings remained unchanged. However, the full extent of the Amadeus incident remains unclear as further information from the technology provider and affected airlines is awaited.